Dave is a marketing expert with 15 years experience in the tech and SaaS world. He specializes in educating IT and channel audiences, with a focus on security, privacy, compliance, and marketing technology. With a talent for storytelling and a deep understanding of the industry, Dave transforms complex IT topics into clear, engaging, and impactful narratives.
Email signature compliance: What IT and legal teams need to know
Key takeaway
Only 55% of organizations give IT clear ownership of email signature management, and that drops to 47% at the enterprise level. The rest are running a shared-ownership problem with no agreed owner.
Manual methods (Exchange transport rules, PowerShell scripts, client-side templates) can't guarantee accuracy, can't stop users from editing disclaimers, and can't produce proof when compliance asks for it.
Centralizing email signature management closes that gap: disclaimers apply automatically after send, updates go out in minutes, and the platform's access logs give you real evidence for audits like ISO 27001 or SOC 2.
Getting this right takes more than a tool. It takes an agreed structure for who owns the wording and who owns the system.
Only 55% of organizations give IT clear ownership of email signature management. At the enterprise level, that drops to 47%, according to Exclaimer's State of Business Email 2025 research. Most of the rest are patching it together as problems come up.
You get a message from Legal: "Can you update our disclaimer in everyone's email signature by tomorrow?" Then Marketing chimes in: "We need a new banner in place before our campaign goes live." Neither team owns the mail environment, but IT is expected to deliver across every user, device, and platform, and when something breaks, the fix lands on your desk.
This blog outlines where the real compliance risks come from, how regulations apply, and why centralized control is the only practical way to keep your organization covered.
The hidden compliance risk in email signatures
Email signatures are easy to overlook. They're not part of a typical IT roadmap. But they go out with every employee email, carrying legal disclaimers, privacy notices, and essential company details.
That puts your organization at legal and reputational risk.
 Without centralized control, you can't confirm what's being sent, and you can't guarantee disclaimers remain intact. When compliance asks for proof they were, there's nothing to show them.
Ed Bodey, Exclaimer's General Counsel, sees this from the legal side: disclaimers carry mandated information across a number of jurisdictions and industries, and "not having them, or not being able to show you had them on particular communications, can cause you an evidence problem."
That leaves IT on the hook to maintain standards without proper systems or ownership. And when compliance issues arise, it's IT that gets pulled in.
What some regulations expect from email signatures
Most regulations don't call out email signatures directly. But what they do require, transparency, accountability, disclosure, is often enforced through them.
The list below isn't exhaustive, but here are a few of the compliance requirements that touch email signatures. The specifics vary, but each one expects your organization to disclose who it is and how it handles data.
Regulation | Region | What it requires |
|---|---|---|
GDPR | Europe | Transparency in how personal data is used, often a privacy statement and policy link |
Directive 2003/58/EC | Europe | Company legal name, registration number, registered office address, place of registration |
HIPAA | U.S. healthcare | Disclaimers reminding recipients that content may be sensitive |
SEC, FINRA, GLBA | U.S. financial services | Disclaimers noting monitoring, that content isn't formal advice, and registration numbers |
PIPEDA | Canada | Disclaimers explaining data handling, privacy officer contact, and opt-out |
GDPR and EU company law (Europe)
The General Data Protection Regulation (GDPR) requires transparency in how personal data is used. Many organizations include a short privacy statement and a link to their full privacy policy.
Directive 2003/58/EC requires business emails to carry the company's legal name, registration number, registered office address, and place of registration.
HIPAA (U.S. healthcare)
Organizations handling protected health information (PHI) include disclaimers required under the Health Insurance Portability and Accountability Act (HIPAA) as a best practice. These statements remind recipients that the content may be sensitive and reinforce internal policy.
UCLA Health was fined $865,500 after staff improperly accessed patients' medical records without authorization. It's a records-access case rather than an email-specific one, but the fine shows how expensive a HIPAA violation gets once regulators get involved, whichever channel it runs through.
FINRA, SEC, GLBA (U.S. financial services)
Firms use disclaimers to show emails may be monitored, that content isn't formal advice, and to provide required registration numbers under rules set by the Securities and Exchange Commission (SEC), the Financial Industry Regulatory Authority (FINRA), and the Gramm-Leach-Bliley Act (GLBA).
Since 2021, the SEC and the Commodity Futures Trading Commission (CFTC) have charged over 100 broker-dealers, investment advisors, and other financial firms with recordkeeping failures tied to employees using unapproved messaging channels, together collecting more than $3 billion in civil penalties. The SEC alone added over $560 million in 2024, across more than 60 firms.
PIPEDA (Canada)
Organizations use email disclaimers to comply with Canada's Personal Information Protection and Electronic Documents Act (PIPEDA), explaining how data is handled, how to contact the privacy officer, or how to opt out.
These support compliance with principles like openness and accountability.
Why manual email signature management breaks under pressure
IT has been patching together email signature management for years, often without the right tools. Whether it's transport rules, PowerShell scripts, client-side templates, or directory-based setups, these methods only go so far. They weren't built for the scale, complexity, or compliance standards organizations are now expected to meet.
Here's where the approach starts to break down.
Scripts and templates can't guarantee accuracy
You can push an update, but it only works if users are on the right client, haven't made local changes, and everything syncs as expected. Even then, there's no way to confirm whether the correct email signature was applied, or when it was last changed.
Admin workarounds don't scale
What starts as a single policy becomes a collection of exceptions: region-specific disclaimers for legal, email banners for marketing, onboarding variations for HR.
Whether you're using Exchange transport rules or Google Admin console settings, these methods get harder to manage with every exception added.
Users keep editing
Even if IT deploys a standard email signature, users can change or remove parts of it in Outlook, Gmail, or on mobile devices, some employees delete disclaimers, others add unapproved content of their own.
Unless email signatures are enforced centrally after the email is sent, there's no guarantee the right information reaches the recipient.
Changes are slow to roll out
When Legal sends an updated disclaimer, IT needs to deploy it to everyone. Without centralized control, that takes time. Once you factor in testing, it can take days. And during the rollout, non-compliant emails are still going out.
There's no audit trail
When compliance asks if the right email disclaimer was in place last quarter, there's no reliable way to confirm it. Whether you run on Exchange Online or Google Workspace, checking individual inboxes or message history isn't audit-ready, and it won't scale when it actually counts.
The result is a time-consuming, error-prone process that can't meet compliance standards. Most IT teams manage disclaimers they didn't write, for standards they don't own.
Why centralizing email signatures solves the compliance gap
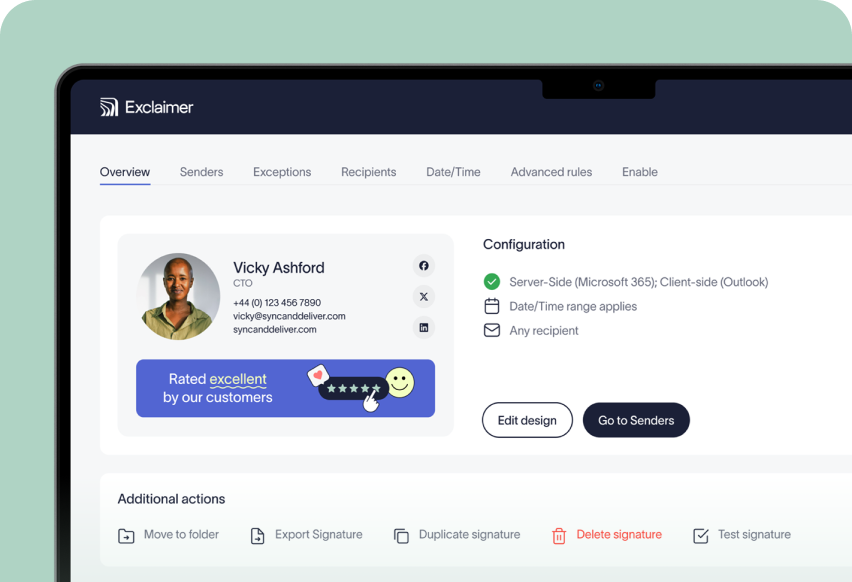
Using a centralized email signature management solution closes the gaps no script can. It gives IT full control, removes day-to-day admin, and gives legal teams the assurance that every email carries the right disclaimer, no exceptions.
Compliance is automatic
Every email gets the correct, approved legal disclaimer, applied after send, across every email on every device. There's no setup required on the end user's side, so there's no reliance on them to follow instructions.
Changes go live in minutes
When legal updates a disclaimer or marketing needs a banner change, you make the update once and it rolls out instantly across the organization. No staggered deployment, no inbox chasing.
Users can't edit protected fields
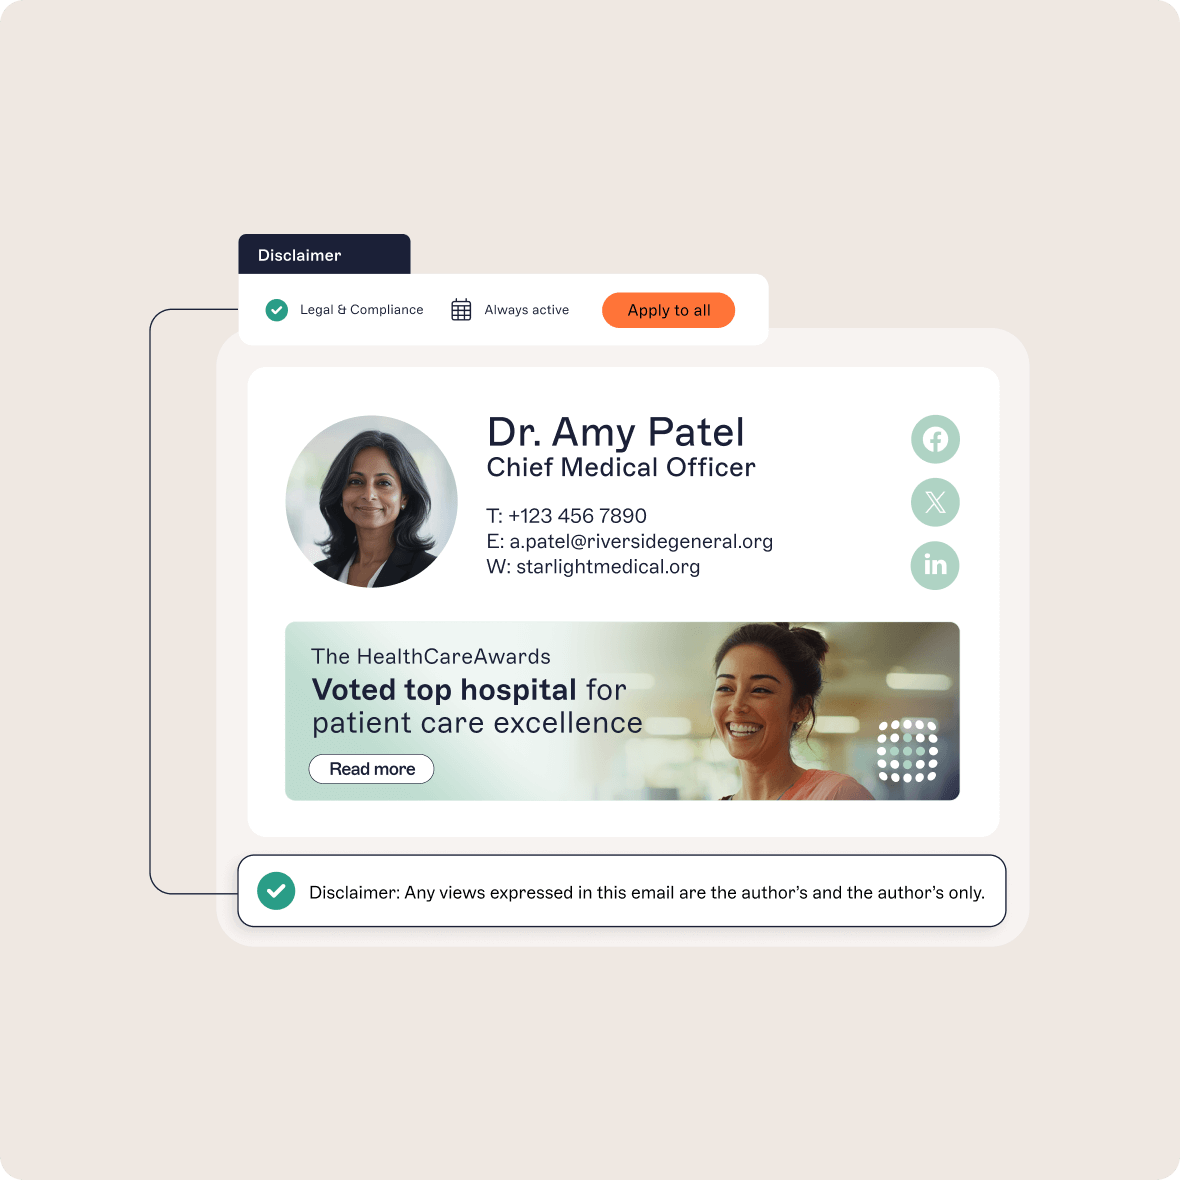
Email disclaimers and regulatory content stay locked, so no one can alter or delete them by accident or on purpose. That gives legal confidence in what's being sent, without IT having to enforce it by hand.
You get an auditable system, not just a policy
Centralized platforms log who accessed the system, and when. That's the evidence auditors actually ask for when you're maintaining certifications like ISO 27001 or SOC 2: a record of who was in the system and when, not just a policy saying they were allowed to be. It isn't a record of every disclaimer sent on every email, and it shouldn't be sold to you as one. What it replaces is worse: no record at all.
Admin overhead disappears
With centralized control, you set email signature policy once instead of maintaining it day to day. You're not fixing formatting issues or chasing last-minute updates.
This is what it looks like when email signatures get treated as part of your infrastructure.
Manual email signature management | Centralized email signature management |
|---|---|
Depends on user setup and behavior | Applies after send, across all platforms |
Requires scripts, templates, and workarounds | Managed through one interface with version control |
No system-level access record | Logged access history |
Changes are slow and error-prone | Updates roll out instantly and consistently |
Best practices for email signature compliance
Centralized control removes the complexity of managing email signatures. But staying compliant also means having the right structure in place: one that reflects legal obligations, industry standards, and how your organization operates.
Keep company details consistent
Every email signature should show the right company name, legal entity type, registration number, and office address. Use a central template to apply this across all teams. It helps you meet business communication laws and avoids regional inconsistencies.
Use a clear confidentiality notice
Even where it's not legally required, a simple statement that the message is confidential and for the intended recipient helps reinforce privacy and reduce legal risk. It matters most for teams handling sensitive or regulated information.
Clarify where responsibility ends
A short line saying your organization isn't liable for actions taken based on the email's content can help reduce exposure. This matters most when emails get forwarded or misread.
Avoid unintended agreements
Add a clear statement that the email doesn't form a contract. This prevents informal replies from being misinterpreted, particularly in procurement, legal, or sales conversations.
Match disclaimers to your industry
Some sectors require specific language. Use dynamic rules so each team's disclaimer matches its own requirements.
Add a privacy statement or link
A sentence referencing your privacy policy, or a link to it, shows transparency. It's not always mandatory, but it demonstrates a clear approach to data protection under regulations like GDPR and PIPEDA.
Make it easy to read
Long blocks of legal text don't get read. Break the disclaimer into short lines, use consistent styling, and keep it separate from contact details so nothing gets missed.
Adapt by team or location
Not every user needs the same disclaimer. Set up versions that change based on region, department, or user group, so you stay compliant without forcing a one-size-fits-all approach.
Agree who owns what
Legal should own the wording. IT should own the system that applies it. A shared process with change control and clear sign-off means updates happen quickly and correctly.
"IT sets the plumbing: the platform, the rules, the governance, the framework. What goes into the signature, the content, the data, the design, should sit with whoever owns those things naturally. HR owns employee data, so HR maintains job titles. Role-based access lets you delegate that without giving up governance. And audit logs matter more than people think. If you're maintaining ISO 27001 or SOC 2, you'll be asked for evidence of changes to your systems, and the audit log is how you provide it."
Make email signature compliance one less thing to worry about
IT owns this system in just over half of organizations today. Centralizing signature management is how the rest close that gap, without the manual workarounds this piece just walked through.
Exclaimer's email signature software gives you full control, with automated updates, centrally applied disclaimers, and a logged record of who accessed the platform and when.
If you're not sure your current setup would hold up the next time an auditor asks who's had access and when, book a demo and find out.