Ed advises technology companies across multiple industries and growth stages, with a focus on helping fast-growing SaaS businesses navigate complex commercial, regulatory, and governance challenges. He's been recognized by Chambers and Partners as "everything you want in a commercial lawyer" and by Legal 500 as "a trusted advisor who is a pleasure to work with."
The deployer's burden: you own everything sent in your name
Key takeaway
Your business answers for everything sent in its name, whether a person or an AI wrote it. Under the EU AI Act, if you put an AI system to work in your business for your own purposes, that makes you the deployer, and the customer's complaint starts with you.
Your AI vendor has its own duties as the provider. They sit one step back from the customer and don't replace yours.
Article 50 of the EU AI Act (Regulation (EU) 2024/1689) has applied since 2 August 2026. Check your supplier contracts and your record of processing activities against the AI tools your teams use. Only the machine-readable marking provider duty for generative AI systems already on the market has grace through to December 2, 2026.
Your business is responsible for everything sent in its name.
What AI has added is a false sense that the technology changes the equation, as though buying a tool built on Anthropic or OpenAI models moves legal weight onto the seller. It doesn't. The law has a name for the company putting an AI system to work in its business for its own purposes (what the EU AI Act calls “under its authority”), and the name is deployer.
Who's liable when AI writes on your behalf?
The company that puts the content out is liable first.
Model providers such as Anthropic feed third-party platforms, those platforms feed the tools a business uses internally, and the output reaches customers under the business's name.
Provider | Deployer | |
|---|---|---|
Who | The developer of the model or AI tool | The business using the AI system for its own purposes |
What the customer sees | Nothing | The company they dealt with |
Where public facing liability starts | One step back | With the deployer |
Roles can overlap. Putting your own name and trademark on an AI system that generates content can bring provider obligations on top of your deployer ones.
What does a failure look like in practice?
Scenario | Who the customer complains to | What decides it |
|---|---|---|
A customer service AI gives wrong information | The business running it | The customer dealt with the business |
A bot or AI-drafted email implies a price or commitment | The business whose name is on it | Whether you can withdraw the error depends on the setup |
A chatbot doesn't say it's AI | The business, then the regulator (the provider carries primary design duty, but the customer still complains to you) | Disclosure of the use of AI has to come at the first interaction at the latest, and be clear and distinguishable |
Air Canada argued that its chatbot was a separate legal entity. In February 2024 a British Columbia tribunal rejected that in Moffatt v Air Canada, 2024 BCCRT 149, held the airline responsible for what the chatbot told a customer (a negligent misrepresentation), and awarded $812.02 in damages, interest and fees.
The tribunal sits outside the EU and the sum is small, but every deployer will be tempted by the same argument. Customers may expect the notice anyway, and 76% of consumers surveyed said they would prefer brands to disclose when AI is used in emails, according to Exclaimer's 2024 personal touch report on AI and email.
That preference matters, and whilst that sentiment will keep moving as new models are released, you should check whether a communication falls within the scope of Article 50(4). This covers deployers’ disclosure obligations in respect of deepfakes and AI-generated text published to inform the public on matters of public interest. It does not apply where a human has reviewed the text and takes editorial responsibility, so ordinary AI-assisted business email will generally fall outside it.
What should legal teams change now?
Most of the work is ordinary governance applied to AI tools.
Review supplier contracts. Providers and deployers can each carry separate transparency duties for one product, so the agreement should say who handles disclosure, and who handles labelling and monitoring.
Map every tool against your AI policy, including AI features switched on inside platforms you already pay for. In many, that takes one click and no regulatory sign-off.
Update your record of processing activities to show where data flows, who processes what, and why. Impact assessments are done per processing activity, not per vendor.
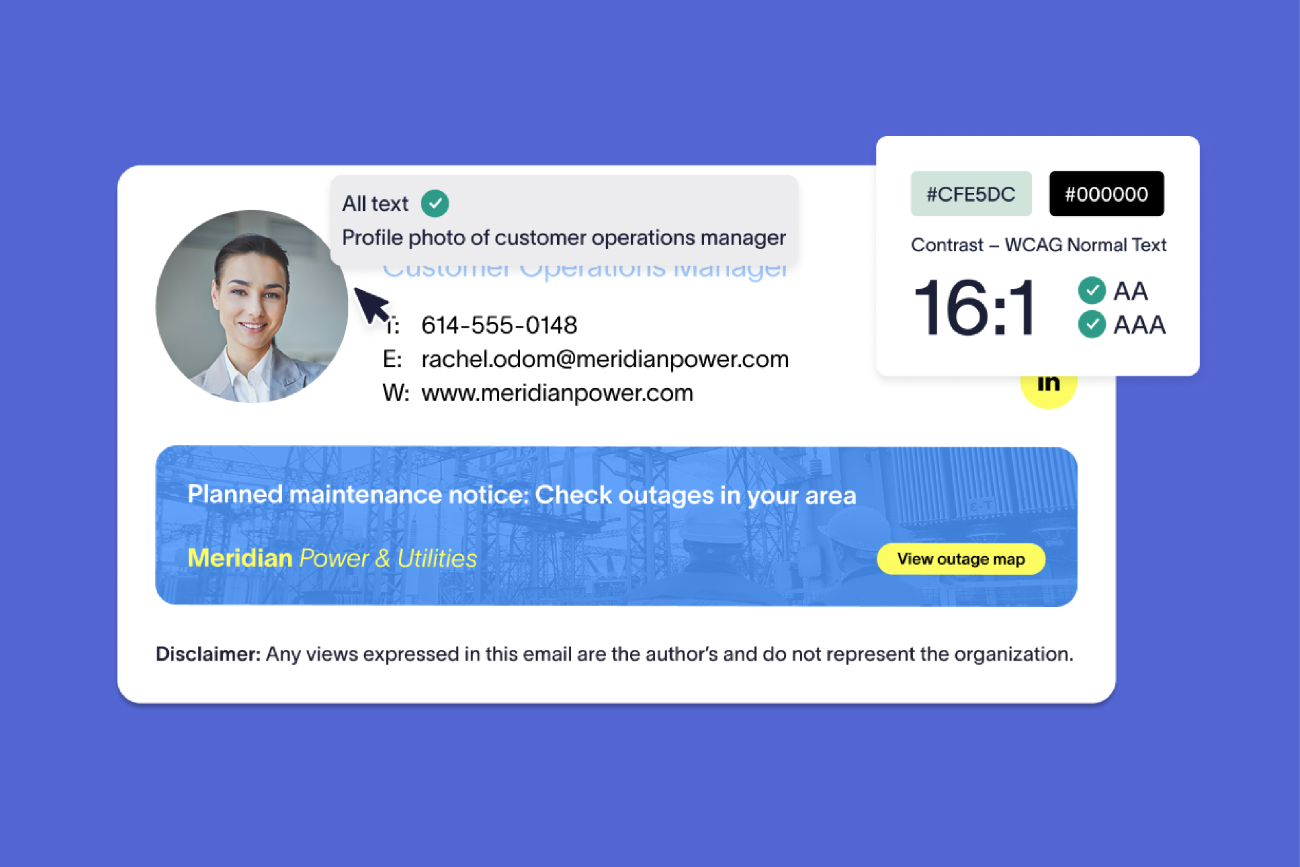
Apply any mandatory or policy-required AI disclaimer text centrally. Exclaimer's cloud solution applies email signatures and disclaimers server-side by rule for Microsoft 365 and Google Workspace, and employees can't edit or remove them. Email compliance in sectors such as financial services starts with that required text – driven by your own policies and sector rules.
Underneath all of this, we're still talking about data. At a previous company, registered under NIS, our incident response plan began by working out which regime applied. Do that for AI before something goes wrong.
Doesn't the vendor carry some of the risk?
The vendor carries its own duties as provider, but the customer's complaint still starts with the deployer.
A provider that ships a chatbot with no AI notice has failed at its end of the supply chain. The customer never sees that chain. They complain to the name on the message, and a regulator or tribunal starts with the company that put the system in front of them. A contract can give you recourse against the vendor afterwards, but the complaint reaches you first.
AI rules were drafted before the rush to large language models, and frontier models now arrive roughly every quarter while the law does not, and cannot, adapt and change at that pace. To my knowledge, there's no enforcement record under the AI Act yet, so nobody can say how a regulator will treat a given failure. Eight to nine years of GDPR practice is the better guide for now.
Where does that leave your governance?
The deployer's burden isn't new. Organizations have always answered for what they communicate, and AI makes it more important to be deliberate about it.
If you can't show which tools write in your name, who approved them, where the data goes and what they send, you have a policy but not governance. If you believe a vendor contract moves the customer's complaint away from you, I'd like to see the clause.
Legal teams that need mandatory disclaimers applied to every outbound email can see how Exclaimer supports legal organizations.